
SSH Keys and Commit Signing: Ed25519, ssh-agent, FIDO2 and Vigilant Mode
Git trusts whatever you type into user.name and user.email. Anyone can make a commit that claims to be from you, push it to a repo they control, and GitHub will show your avatar next to it. Meanwhile the SSH key that does prove who's pushing has often sat unencrypted in ~/.ssh since a laptop three jobs ago.
Both problems take about fifteen minutes to fix, and in 2026 the same Ed25519 key can handle authentication and commit signing. Here's the setup I'd give a new teammate, with every command taken from GitHub Docs or the OpenSSH manuals.
Generate an Ed25519 key with a passphrase
ssh-keygen -t ed25519 -C "[email protected]"That's the command GitHub Docs gives. On current OpenSSH you could drop -t entirely: OpenSSH 9.5 (October 2023) made ssh-keygen "generate Ed25519 keys by default." GitHub's fallback for systems without Ed25519 is ssh-keygen -t rsa -b 4096, which you should only need on very old servers.
Two things worth knowing from the ssh-keygen manual:
- Keys are written in OpenSSH's own format, which protects a passphrase-encrypted key better than the old PEM format.
-asets the number of bcrypt KDF rounds used on the passphrase (default 32). The manual says higher numbers mean slower passphrase checks and more resistance to brute-force cracking "should the keys be stolen." - If you already have a key and it has no passphrase, add one without regenerating:
ssh-keygen -p -f ~/.ssh/id_ed25519.
Set the passphrase. A private key file with no passphrase is a bearer credential to every server and repo it's registered on; anyone who copies that one file from a backup, a stolen laptop or a compromised dependency's postinstall script has it.
As of November 2026, the current OpenSSH release is 10.6p2 (5 November 2026). Since 10.0, DSA support is gone and the hybrid post-quantum key exchange mlkem768x25519-sha256 is the default for key agreement, so keeping your client current also keeps your transport modern. GitHub no longer accepts DSA keys either.
Our SSH key generator produces Ed25519 and RSA pairs in the browser with the Web Crypto API, which is handy for test fixtures and throwaway CI keys. For a key that guards real access, I'd still run ssh-keygen on the machine that will hold it, so the private key never exists anywhere else.
Let ssh-agent hold the passphrase
Typing the passphrase on every git fetch gets old fast, which is why people skip it. ssh-agent holds the decrypted key in memory instead. On macOS, GitHub's recommended ~/.ssh/config:
Host github.com
  AddKeysToAgent yes
  UseKeychain yes
  IdentityFile ~/.ssh/id_ed25519
then once:
ssh-add --apple-use-keychain ~/.ssh/id_ed25519GitHub notes this needs Apple's bundled ssh-add, not a Homebrew one. On Linux, eval "$(ssh-agent -s)" and ssh-add ~/.ssh/id_ed25519, or let your desktop's keyring do it.
A few agent options from the ssh-add and ssh_config manuals that are worth turning on:
ssh-add -t 8hsets a lifetime, so the key drops out of the agent at the end of the day.ssh-add -casks for confirmation each time the key is used. Annoying for signing every commit, useful for a production-access key.IdentitiesOnly yesunder aHostblock makes ssh offer only the key you configured, not every key in the agent.ForwardAgent: the manual says agent forwarding "should be enabled with caution," because anyone who can get around file permissions on the remote host can use your agent through the forwarded connection. PreferProxyJumpfor hopping through a bastion; it doesn't hand your agent to the middle box.
Hardware-backed keys (FIDO2)
OpenSSH 8.2 (February 2020) added FIDO/U2F authenticator support via two key types, ed25519-sk and ecdsa-sk. Per those release notes, the device's private key "cannot be exported from the token hardware"; the file in ~/.ssh holds only a key handle, and the token must be attached whenever the key is used.
ssh-keygen -t ed25519-sk -C "[email protected]"
# if the token doesn't support Ed25519, GitHub suggests:
ssh-keygen -t ecdsa-sk -C "[email protected]"
The -O options in the ssh-keygen manual let you tune it:
| Option | Effect |
|---|---|
-O resident | Store the key handle on the authenticator, so you can load it on a new machine with ssh-add -K |
-O verify-required | Require user verification (PIN or biometric) for every signature, not just a touch |
-O application=ssh:work | Override the default ssh: application string |
-O no-touch-required | Skip the touch requirement (defeats much of the point; avoid) |
GitHub's docs say the device must stay connected while you authenticate. My suggestion: a hardware key for anything with production or admin access, and an ordinary passphrase-protected Ed25519 key for day-to-day git if touching a token on every push would drive you to disable it. If hardware keys interest you for web logins too, our password security post covers passkeys.
Sign commits with the SSH key you already have
GitHub supports three signature types: GPG, SSH and S/MIME. Its commit signature docs say "SSH signatures are the simplest to generate," and you can reuse your authentication key. It requires Git 2.34 or later.
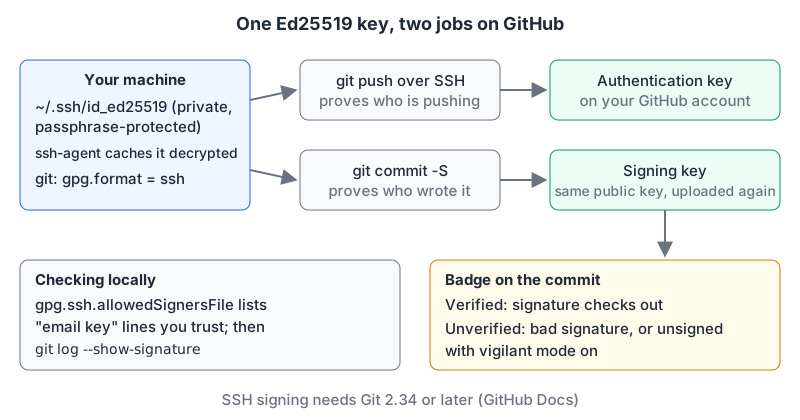
The setup, from Telling Git about your signing key:
git config --global gpg.format ssh
git config --global user.signingkey ~/.ssh/id_ed25519.pub
git config --global commit.gpgsign true
git config --global tag.gpgSign true
Then upload the same public key a second time on GitHub, choosing Signing Key as the key type. GitHub's adding a key page notes a key used for both jobs has to be added twice. With the CLI:
gh ssh-key add ~/.ssh/id_ed25519.pub --type signingMake sure the email in your commits is a verified address on your account, or GitHub can't tie the signature to you.
To verify SSH signatures locally, Git needs to know which keys to trust. The git-config docs describe gpg.ssh.allowedSignersFile as a file of principals followed by a public key:
echo "[email protected] $(cat ~/.ssh/id_ed25519.pub)" >> ~/.config/git/allowed_signers
git config --global gpg.ssh.allowedSignersFile ~/.config/git/allowed_signers
git log --show-signature -1
The same docs note that since OpenSSH 8.8 the file can carry valid-after and valid-before options, which is how you express "this key was valid until we rotated it."
SSH signing or GPG?
GitHub itself frames the trade-off: GPG takes more work to set up, but "GPG has features that SSH does not," namely key expiry and revocation that show up in the signature status.
| SSH signing | GPG signing | |
|---|---|---|
| Setup | Reuse your existing key; four git config lines | Generate a key with gpg --full-generate-key, export, upload |
| Git version | 2.34+ | Any |
| Expiry and revocation | Not in the key; valid-after/valid-before in allowed_signers for local checks | Built into the key, reflected in GitHub's status |
| Passphrase caching | ssh-agent, Keychain on macOS | gpg-agent; GitHub notes it doesn't integrate with Keychain like ssh-agent, so many people use GPG Suite or Gpg4win |
For an individual or a team on GitHub, I'd pick SSH signing. The setup friction of GPG is the main reason people never sign anything, and one key to protect beats two. Pick GPG if you already have an OpenPGP identity with subkeys, need signatures that other tooling verifies through the web of trust, or want revocation visible on GitHub.
Also note what verification on GitHub means after a rotation. Per GitHub, "once a commit signature is verified, it remains verified within its repository's network," even if you later remove or rotate the key. So rotating a key doesn't turn your history red.
Turn on vigilant mode, but only after you sign everything
Signing your own commits doesn't stop someone else from pushing unsigned commits under your email. Vigilant mode closes that gap: with it on, every commit attributed to you gets a status, and unsigned ones are marked Unverified. There's also Partially verified, when a signed commit lists a co-author who has vigilant mode on but isn't the committer, because the signature doesn't prove that co-author agreed.
Enable it under Settings, then SSH and GPG keys, then "Flag unsigned commits as unverified." GitHub's warning is the important bit: "You should only enable vigilant mode if you sign all of your commits and tags." Set commit.gpgsign true on every machine you commit from first, including that old desktop, or your own pushes start showing up as Unverified.
The fifteen-minute checklist
ssh-keygen -t ed25519, with a passphrase. Add one to old keys withssh-keygen -p.- Agent with a lifetime (
ssh-add -t),IdentitiesOnly yes, no blanketForwardAgent. - Delete stale keys from GitHub and from
~/.ssh/authorized_keyson servers you manage. - Hardware
-skkey for production and admin access. gpg.format ssh,user.signingkey,commit.gpgsign true,tag.gpgSign true, then upload the key as a Signing Key.- An
allowed_signersfile sogit log --show-signatureworks locally. - Vigilant mode, once every machine signs.
If your team is deciding between hosts, our GitHub vs GitLab comparison is a good next read, and the Git command generator helps when you can't remember the flag for something rarer.
Written by AIDToolStack Editorial
Researched from official documentation, specifications and vendor pages, listed under Sources below. Last checked November 2026.
Sources
- docs.github.com/en/authentication/connecting-to-github-with-ssh/generating-a-new-ssh-key-and-adding-it-to-the-ssh-agent
- www.openssh.org/txt/release-9.5
- man.openbsd.org/ssh-keygen
- www.openssh.org/releasenotes.html
- docs.github.com/en/authentication/connecting-to-github-with-ssh/adding-a-new-ssh-key-to-your-github-account
- man.openbsd.org/ssh-add
- man.openbsd.org/ssh_config
- www.openssh.org/txt/release-8.2
- docs.github.com/en/authentication/managing-commit-signature-verification/about-commit-signature-verification
- docs.github.com/en/authentication/managing-commit-signature-verification/telling-git-about-your-signing-key
- git-scm.com/docs/git-config
- docs.github.com/en/authentication/managing-commit-signature-verification/displaying-verification-statuses-for-all-of-your-commits
- git-scm.com/docs/git-log
- docs.github.com/en/authentication/managing-commit-signature-verification/generating-a-new-gpg-key
- docs.github.com/en/authentication/managing-commit-signature-verification/signing-commits
Related Posts
Explore on AIDToolStack
Discover tools and servers featured in our directory.
AI Tools
MCP Servers
Sponsor Our Newsletter
Reach thousands of developers who are actively evaluating AI tools, MCP servers, and dev infrastructure. Our weekly newsletter goes to engaged technical decision-makers.
All sponsored content is clearly labeled per our editorial policy.