
Automating Dependency Updates Without Breaking Things: Dependabot and Renovate
You turn on Dependabot on Monday. By Wednesday there are 23 open PRs, half of them failing for the same reason, and the team has learned to ignore the bot entirely. Six months later you're four majors behind on your framework and a security fix needs an upgrade path nobody has walked.
Automated updates fail in two opposite ways: too much noise, so nobody merges, or too much trust, so something broken (or malicious) merges at 3 a.m. The fix for both is the same set of settings, and Dependabot and Renovate both have them as of November 2026. This post walks through grouping, schedules, a release-age delay, automerge rules and lockfile maintenance, with config for each tool.
Dependabot or Renovate
| Dependabot | Renovate | |
|---|---|---|
| Where it runs | Built into GitHub | GitHub, GitLab, Bitbucket, Azure DevOps, Gitea, Forgejo, hosted or self-hosted |
| Config | .github/dependabot.yml | renovate.json, .github/renovate.json and a few other names |
| Grouping | groups per ecosystem, plus multi-ecosystem-groups | packageRules with groupName, presets like group:monorepos |
| Release-age delay | cooldown, default 3 days for version updates | minimumReleaseAge, off unless you set it or use a preset |
| Automerge | Not built in; a GitHub Actions workflow enables auto-merge | automerge per rule, native or Renovate-driven |
| Lockfile refresh | No dedicated option | lockFileMaintenance |
My take: if you're on GitHub and want something running this afternoon, Dependabot is fine and getting better. If you want fine-grained rules (automerge dev tools but not runtime deps, delay npm but not Docker, a dashboard of pending updates), Renovate is the more capable tool. Our Dependabot config generator and Renovate config generator produce a starting file for either.
1. Group updates so the PR count is survivable
Without groups, every outdated dependency gets its own PR. Dependabot's options reference lets you combine them by name pattern, dependency type (development or production, for ecosystems such as npm, pip, bundler and maven) and update type:
version: 2
updates:
  - package-ecosystem: "npm"
    directory: "/"
    schedule:
      interval: "weekly"
      day: "monday"
      time: "06:00"
      timezone: "Europe/London"
    open-pull-requests-limit: 5
    groups:
      dev-tooling:
        dependency-type: "development"
        update-types: ["minor", "patch"]
      prod-minor-patch:
        dependency-type: "production"
        update-types: ["minor", "patch"]
  - package-ecosystem: "github-actions"
    directory: "/"
    schedule:
      interval: "weekly"
A dependency that matches more than one group goes into the first match, so order groups from most to least specific. Majors aren't in any group above, which is deliberate: each major gets its own PR, so one breaking upgrade can't hold twenty safe ones hostage. Groups can also apply to security updates with applies-to: security-updates.
In Renovate, config:recommended already includes group:monorepos and group:recommended (per the presets docs), so packages released together, such as a framework's family of packages, arrive as one PR. Add your own with packageRules and groupName.
2. Schedule the noise and cap it
Dependabot's schedule.interval accepts daily, weekly, monthly, quarterly, semiannually, yearly or cron (with a cronjob expression). If you don't set a time, it picks one at random; times are UTC unless you set timezone. open-pull-requests-limit defaults to 5 for version updates. Security updates have their own fixed limit of 10, which the setting doesn't change.
Renovate's schedule takes cron syntax (the Later text syntax still works but is deprecated). Two details from its docs: minutes must be * because Renovate doesn't schedule to the minute, and a schedule doesn't trigger a run, it only permits one. Renovate recommends a window of at least 3 to 4 hours so a run actually lands inside it:
{
  "schedule": ["* 0-5 * * 1"],
  "prConcurrentLimit": 10,
  "prHourlyLimit": 2
}
Renovate always creates security PRs even when the concurrent limit is reached.
3. Wait before you take a new release
This is the setting that changed most in the last year, and the reason is supply-chain attacks. In September 2025 CISA issued an alert about the Shai-Hulud worm, which had compromised over 500 npm packages. It harvested credentials such as GitHub tokens and cloud API keys from the machines that installed it, then used stolen npm credentials to publish infected versions of other packages. Among CISA's recommendations: pin dependencies to known-safe releases from before the compromise and enable Dependabot security updates.
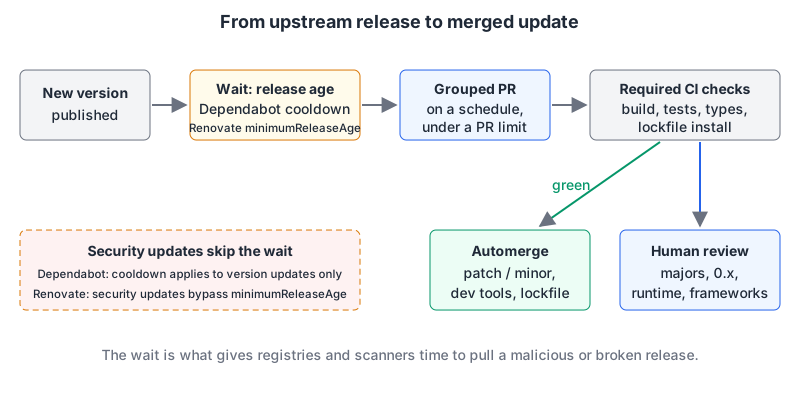
A bot that installs every release the minute it's published is exactly how a worm like that reaches your CI secrets. A release-age delay gives the registry, maintainers and scanners time to catch and pull a bad version first.
Dependabot calls it cooldown. Per the options reference, if you don't specify it, Dependabot applies a default 3-day cooldown to version updates. You can tune it per SemVer level:
    cooldown:
      default-days: 3
      semver-major-days: 14
      semver-minor-days: 7
      semver-patch-days: 3
      exclude:
        - "@acme/*"
The per-level keys aren't supported for some ecosystems (Docker, GitHub Actions and Terraform among them), where default-days applies. include and exclude take up to 150 patterns each. Cooldown never applies to security updates.
Renovate calls it minimumReleaseAge. It's off in config:recommended; config:best-practices adds security:minimumReleaseAgeNpm, which waits three days for npm packages. Or set it yourself:
{
  "packageRules": [
    { "matchDatasources": ["npm"], "minimumReleaseAge": "3 days" }
  ],
  "internalChecksFilter": "strict"
}
While a release is younger than the threshold, Renovate puts a pending renovate/stability-days status check on the branch, which also stops automerge. The docs recommend internalChecksFilter: "strict" alongside it so you don't get PRs for versions still in the waiting period. The config docs add a second reason for npm: packages less than 72 hours old can be unpublished from the registry. Security updates bypass the delay.
Your package manager can enforce the same idea at install time. pnpm's minimumReleaseAge is measured in minutes, with a built-in default of 1440 (one day). Renovate's docs suggest setting the age in both places, and Renovate adds a 30-minute minimumReleaseAgeBuffer by default so packages published shortly after the main one don't trip the package manager's own check.
4. Automerge only what CI can vouch for
Automerge is safe exactly to the extent your required checks would catch a breaking update. If your test suite doesn't exercise a dependency, automerging it is just merging without reading.
Renovate has it built in. The automerge docs suggest starting with updates you'd merge anyway, such as dev tooling and lockfile maintenance, and give this rule for non-major updates that skips 0.x packages (where SemVer allows breaking minors):
{
  "packageRules": [
    {
      "matchUpdateTypes": ["minor", "patch"],
      "matchCurrentVersion": "!/^0/",
      "automerge": true
    }
  ]
}
With platformAutomerge (the default) Renovate uses GitHub's native auto-merge. The config docs carry a warning: if branch protection requires status checks, select at least one specific check, or GitHub might automerge PRs with failing tests. automergeType: "branch" skips the PR entirely and pushes to the base branch when tests pass, which won't work if branch protection blocks direct pushes.
Dependabot has no automerge setting. GitHub's documented approach is a workflow that reads the PR's metadata and enables auto-merge for the update types you choose. A trimmed version of their example, broadened to patch updates of any dependency:
name: Dependabot auto-merge
on: pull_request
permissions:
  contents: write
  pull-requests: write
jobs:
  dependabot:
    runs-on: ubuntu-latest
    if: github.event.pull_request.user.login == 'dependabot[bot]'
    steps:
      - id: metadata
        uses: dependabot/fetch-metadata@d7267f607e9d3fb96fc2fbe83e0af444713e90b7
        with:
          github-token: "${{ secrets.GITHUB_TOKEN }}"
      - if: steps.metadata.outputs.update-type == 'version-update:semver-patch'
        run: gh pr merge --auto --merge "$PR_URL"
        env:
          PR_URL: ${{ github.event.pull_request.html_url }}
          GH_TOKEN: ${{ secrets.GITHUB_TOKEN }}
This only sets the PR to merge once requirements are met, so it depends on auto-merge being enabled for the repo and on "Require status checks to pass before merging" in branch protection. If the branch uses a merge queue, the docs note GITHUB_TOKEN can't add PRs to it; use a GitHub App token or PAT for that step. The action is pinned to a commit SHA, as GitHub's example does, which is the right habit for any third-party action. More on that in GitHub Actions CI/CD patterns.
5. Refresh the lockfile on purpose
Updating direct dependencies leaves transitive ones wherever the lockfile last resolved them. Renovate's lockFileMaintenance deletes the lockfile, lets the package manager regenerate it with the latest versions your ranges allow, and opens a PR. It's disabled by default, runs "before 4am on monday" when enabled, and pairs well with automerge:
{
  "lockFileMaintenance": { "enabled": true, "automerge": true }
}
config:best-practices includes :maintainLockFilesWeekly, and the security:minimumReleaseAge* presets exempt lockfile maintenance from the release-age delay, so set your own minimumReleaseAge on it if that matters to you. Dependabot has no equivalent option, so on Dependabot-only repos a periodic manual npm update (or your package manager's equivalent) in its own PR covers similar ground.
Gotchas
- Majors rot if nobody owns them. Keep them out of automerge and out of groups, and give someone a recurring slot to work through them. Renovate's Dependency Dashboard (in
config:recommended) gives you the list. - Grouping hides the culprit. When a grouped PR fails, you'll bisect inside it. Keep production groups smaller than dev-tool groups.
- CI that only runs on
pull_requestdoesn't run on Renovate's branch-automerge branches. Renovate's docs say to includerenovate/**in your workflow triggers for that mode. - Don't automerge GitHub Actions bumps on SHA-pinned workflows without reading them; an action has the same access to your secrets as your own code.
- Security alerts are separate. Turn on Dependabot alerts or Renovate's vulnerability alerts so a CVE fix isn't sitting behind a weekly schedule. Our web security checklist has the other supply-chain controls.
A starting policy: weekly schedule, grouped minor and patch by dependency type, a 3-day release-age delay (longer for majors), automerge for dev tooling, lockfile maintenance and non-0.x patches with required checks on, and humans for everything else.
Written by AIDToolStack Editorial
Researched from official documentation, specifications and vendor pages, listed under Sources below. Last checked November 2026.
Sources
- docs.github.com/en/code-security/dependabot/working-with-dependabot/dependabot-options-reference
- docs.github.com/en/code-security/dependabot/working-with-dependabot/automating-dependabot-with-github-actions
- docs.renovatebot.com/modules/platform/
- docs.renovatebot.com/configuration-options/
- docs.renovatebot.com/presets-config/
- docs.renovatebot.com/key-concepts/minimum-release-age/
- docs.renovatebot.com/key-concepts/automerge/
- www.cisa.gov/news-events/alerts/2025/09/23/widespread-supply-chain-compromise-impacting-npm-ecosystem
- pnpm.io/settings/dependency-resolution
Related Posts
Explore on AIDToolStack
Discover tools and servers featured in our directory.
AI Tools
MCP Servers
Sponsor Our Newsletter
Reach thousands of developers who are actively evaluating AI tools, MCP servers, and dev infrastructure. Our weekly newsletter goes to engaged technical decision-makers.
All sponsored content is clearly labeled per our editorial policy.